Control failure stays visible
A failed or contradicted obligation cannot be silently averaged into a positive posture or disguised as absence of data.
Five-stage governing doctrine
The Assurance Chain is a deliberate separation of observations, applicable obligations, proof, tested assurance conclusions and accountable posture decisions. Each stage answers a different question.
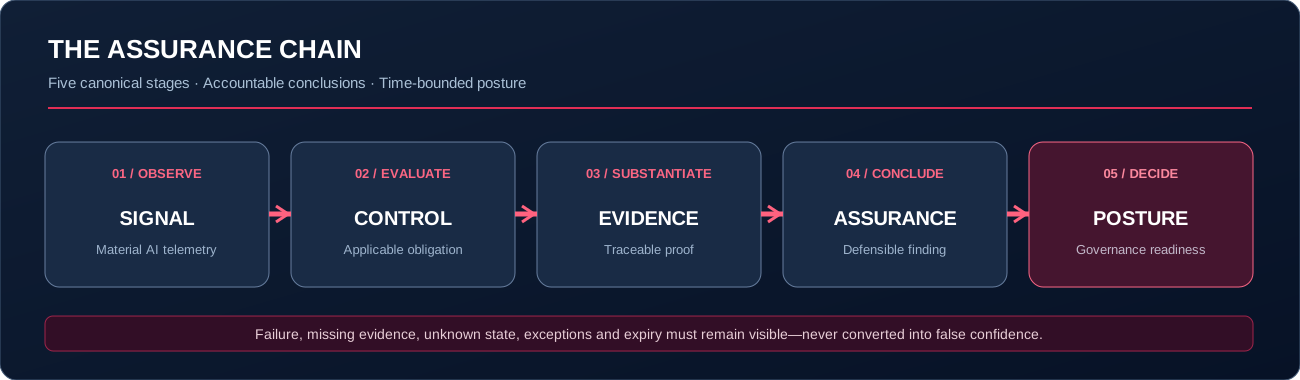
SIGNAL → CONTROL → EVIDENCE → ASSURANCE → POSTURE
Observe relevant events, inventories and changes across AI, identity, cloud, data and security systems. A signal begins an assessment; it is not itself a control conclusion.
Remediation, approval and revalidation are related governance processes—not additional Assurance Chain stages.
STATE SEMANTICS
A failed or contradicted obligation cannot be silently averaged into a positive posture or disguised as absence of data.
Uncollected, expired or incomplete proof must remain a material qualification to the resulting conclusion.
Ambiguous ownership, provenance, runtime state or provider signals require challenge and defined treatment—not guessed control effectiveness.
WORKED CONCEPTUAL TRACE
Illustrative scenario only—not a live system test, customer claim or production-qualified capability.
The event identifies the agent, tool, target resource, time, purpose and available identity context.
The applicable requirement tests whether permission and delegation match approved scope and policy.
Identity grants, policy revisions, activity traces, denial/allow outcome and provenance are associated with the test.
Assess whether both permitted and prohibited paths behaved as intended and whether coverage is sufficient.
Record the result, unknowns, exceptions, accountable approver and the change that requires revalidation.
ARCHITECTURAL INDEPENDENCE
Cloud, identity, runtime, GRC and AI services are sources of truth for their own records. A licensed implementation of AISPG may link these records into traceable assurance and governance conclusions. The availability, quality and timeliness of each source must be verified independently.
Evidence is necessary. Qualified assurance is the reason it can support a decision.
AISPG™ governing principle
THE NEXT CONVERSATION
Explore how AI Runway™ connects the strength of that argument to enterprise investment decisions.
EXPLORE THE NEXT LEVEL
Request approved governance material, a strategic dossier or a scoped architectural discussion.
Enter the Documentation Center ↗